

仮想通貨取引所も警戒、PHPに重大脆弱性|遠隔操作の恐れ
よきょい
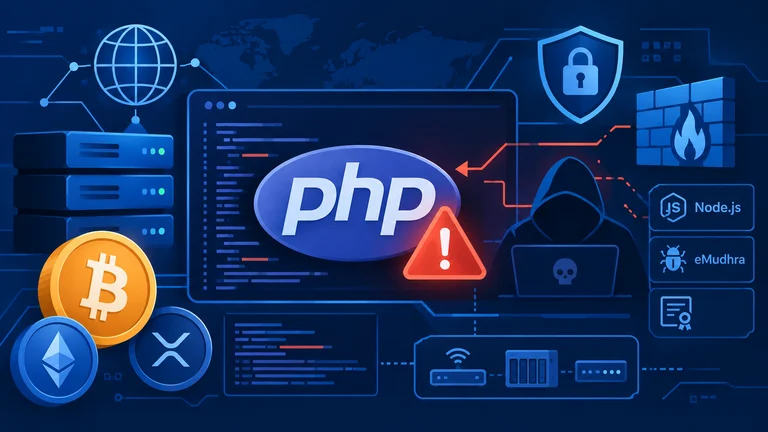


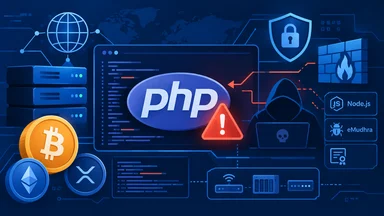
ウェブ開発で広く使われるプログラミング言語PHPの開発チームは10月21日、認証なしで遠隔からコードを実行される恐れがある重大な脆弱性2件(CVE-2026-109618、CVE-2026-109619)を修正しました。
PHP2Shell update before the 10 AM ET patch:
@Cloudflare CTO @dok2001 says they're already seeing early attacks against the two leaked PHP RCE bugs (CVE-2026-109618 and CVE-2026-109619). WAF rules are live for all plans, including free, but he calls it a stopgap.
If you run PHP on anything internet facing:
Patch the moment @ThePHPF ships at 14:00 UTC.
If you can't patch today, take it offline or put it behind a WAF.
Make sure your origin isn't reachable directly, or the WAF does nothing.
After patching, look for web shells, new admin users and modified PHP files.The servers you know about will get patched today. The harder part is where else PHP hides: routers, NAS boxes, firewalls, control panels and vendor appliances. Many of those only get fixed when the vendor ships firmware, and some never will. Find them, and if they face the internet, cut them off until there's a fix.
— Nick Percoco (@c7five) October 21, 2026
仮想通貨取引所クラーケンの最高セキュリティ責任者(CSO)ニック・パーココ氏は、すぐにパッチを適用できない場合はシステムをオフラインにするよう求めました。あるいはWAF(ウェブアプリケーションファイアウォール、不正な通信を遮断する仕組み)の背後に置くべきだとしています。
パッチ適用後も不正な管理者アカウントや改ざんされたファイル、ウェブシェル(遠隔操作用の不正プログラム)が残っていないか調べる必要があるとしました。さらにルーターやNAS、ファイアウォールなどに組み込まれたPHPはメーカーの更新に頼るしかなく、更新が届かない機器もあると警告しています。
ハードウェアウォレット大手レジャーの最高技術責任者(CTO)シャルル・ギユメ氏は、複数の脅威が重なっている点を指摘しました。
Imagine you wake up and:
- PHP has two critical vulnerabilities, rated 9.2, and exploitation has already started, even before the fix was published. There's not fix for old versions... https://t.co/OrhEWKjwDz
- Node.js has four high vulnerabilities, including arbitrary code execution. https://t.co/LQdFMWmNPE
- Eight TLS intermediates have private keys of 3 to 8 bits. I don't believe in conspiracy theories, but... https://t.co/syUV8gdZoIAll of this is in the field. Millions of machines are vulnerable. Most of them will not be patched in the near future and you can't really trust TLS anymore...
The state of security is really, really frightening. And it won't get better anytime soon. 🫠
— Charles Guillemet (@P3b7_) October 21, 2026
PHPに加え、Node.jsの高深刻度の脆弱性修正やインドの認証事業者eMudhraの中間証明書8件の侵害が同時期に発生しています。これらの証明書は秘密鍵が極めて弱く、正規のサービスになりすまされる恐れがあるため、モジラは10月17日にFirefoxで該当証明書を無効化しました。
PHPの開発チームはサポート終了済みの7.4、8.0、8.1向けにも最小限の修正を提供しましたが、更新こそが唯一の完全な対策だとしています。取引所やウォレット事業者は相互に接続されたサーバーや管理画面、外部のインフラに依存しているため、影響は公開ウェブサイトにとどまりません。
見落とされがちな周辺機器まで点検できるかが、業界の安全性を左右することになりそうです。

Ether.fiカードは普段のお買い物からネットショッピングまで、Visa加盟店で幅広く使える仮想通貨クレジットカードです。対象のカード決済で3%のキャッシュバックが受けられます。
仮想通貨を国内の取引所で日本円に換えて銀行口座へ出金する。そんな手間を省いて、日常の支払いをもっとスムーズに。
現在、エントリーモデルの年会費は無料なので是非この機会に登録してみましょう!
Ether.fiカードとは?
Ether.fiカードは普段のお買い物からネットショッピングまで、Visa加盟店で幅広く使える仮想通貨クレジットカードです。対象のカード決済で3%のキャッシュバックが受けられます。
仮想通貨を国内の取引所で日本円に換えて銀行口座へ出金する。そんな手間を省いて、日常の支払いをもっとスムーズに。
現在、エントリーモデルの年会費は無料なので是非この機会に登録してみましょう!
Ether.fiカードとは?
Triaカードは世界中で使える仮想通貨クレジットカードで、最大6%が仮想通貨でキャッシュバックされます。
資産運用や最大40倍レバレッジの仮想通貨取引も同一のカード管理アプリから行えます。「バーチャルカードプラン」は期間限定割引となっているため是非この機会に登録しておきましょう。(登録に必要なアクセスコード:MWVJXJ6475)
Triaの特徴
Pick up
ニュース/解説記事
-

ALL
-

NFT
-

Web3ゲーム
-

DeFi
-

取引所